Cyclone 365

Dependable Service. Consistent Results.

With over 25 years of industry experience, we provide a wide range of IT services for small and medium-sized businesses on the Gulf Coast.

Open weekdays from 9am to 5pm.

In-person office meetings by appointment only.

When to Replace Your Business Computers
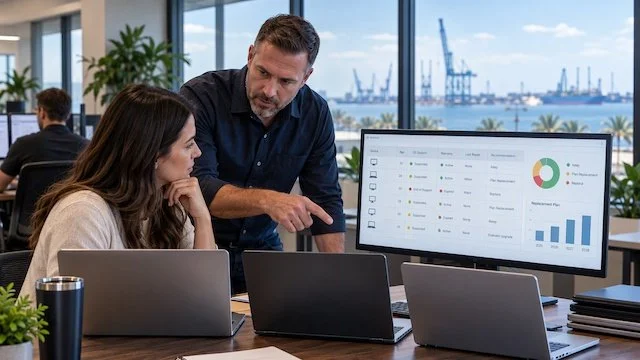
Most business computers don’t fail all at once. A laptop may still handle email and documents while taking longer to start, struggling during video calls, or running out of battery halfway through the day. Those small frustrations add up quickly, and they’re usually the first sign that a device is nearing the end of its useful life.

For most office computers, three to five years is a sensible replacement range. Start reviewing each device once it reaches three years old, then decide whether to replace it soon or keep it another year or two. Dell recommends refreshing business computers every three to four years, and Intel’s refresh program uses a similar three-year benchmark. These are planning guidelines, not expiration dates. A secure, reliable three-year-old laptop doesn’t need to be replaced simply because of its age.

Security Support Comes First

Before you look at speed or battery life, confirm the computer can run an operating system that still receives security updates. Once an operating system reaches end of support, newly discovered vulnerabilities may never be patched. Security software helps, but it can’t correct every weakness in the unsupported system underneath it. A computer can be perfectly reliable and still need replacing because its hardware won’t support a current operating system. Cyclone 365 reviews operating system support status across client environments so Gulf Coast businesses aren’t caught off guard by a deadline they didn’t see coming.

Match the Computer to the Work

An employee who mainly uses email, documents, and browser-based applications may be perfectly comfortable on an older machine. Someone working with large spreadsheets, design files, video, or engineering software likely needs newer hardware. Review performance while the employee is doing their actual work, and ask how often the computer interrupts them. A slow startup once a week is very different from delays throughout the day.

Slow Doesn’t Always Mean Old

Poor performance has many causes. A full storage drive, insufficient memory, unnecessary startup programs, malware, overheating, or a failing drive can all make a computer crawl. Have the cause identified before approving a replacement. Maintenance, added memory, or a new storage drive may restore normal performance for a fraction of the cost. That said, spending money on an upgrade makes little sense if the device will soon lose operating system support or if other components are already failing.

Repairs, Warranties, and Parts

One repair rarely justifies a replacement, but repeated repairs change the math. Add up repair bills, support charges, and the hours an employee couldn’t work normally. A repair that looks cheaper than a replacement can be poor value if another failure is likely. Warranty expiration is a good moment to review a device rather than an automatic reason to replace it, though parts availability matters a great deal when you don’t keep spares on hand. Along the Gulf Coast, where a single storm can disrupt a week of productivity, having a prepared spare device ready to go is worth the investment.

Plan Ahead Instead of Reacting

Keep a record of each computer’s purchase date, model, assigned user, warranty expiry, operating system, and next review date. Assign a planned replacement year based on what you find, and spread purchases across budget periods rather than replacing a large group all at once. Standardizing on a small number of approved models also simplifies everything, letting employees share compatible docks and chargers while your IT provider maintains consistent security settings.

Wipe the Data Before It Leaves

Deleting files or removing a user account does not guarantee business data is gone. Storage should be properly sanitized before any computer is sold, donated, recycled, or discarded, using a method appropriate to the drive type and the sensitivity of the information. NIST Special Publication 800-88 Revision 2, published in September 2025, provides current guidance. Keep a disposal record with the asset number, serial number, disposal date, and method used.

If you’re not sure where your computers stand, Cyclone 365 can review the age, support status, and condition of every device in your business and build a replacement schedule that fits your budget. Reach out and we’ll help you sort it out. Call or Email us today!
When Hackers Turn a Freezer Into an Oven

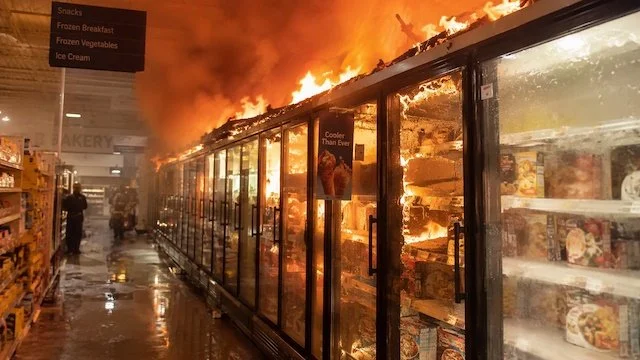
Over the past three months, a strange new kind of cyberattack has been spreading. In August, freezers at at least six US military base commissaries flipped into defrost mode overnight and cooked the food inside. On the night of October 11, hundreds of French supermarkets, including Intermarché, Carrefour and Monoprix, had their refrigeration pushed to 122°F. Millions of euros of food spoiled and some units caught fire. On November 2, a second wave hit stores in Belgium, Ireland, Sweden, the Netherlands, Luxembourg, Estonia and Finland.

Here is the part business owners need to understand. The attackers never touched a single freezer. They went after the central controller that runs all of a store’s refrigeration, the same box a maintenance contractor logs into remotely. Those controllers were sitting wide open on the public internet. Once inside, the attackers forced defrost cycles and raised temperature setpoints. In France, reporting indicates they also stretched the defrost cycle from one hour to eight so the alarms never fired.

The way in was almost embarrassingly simple. A security researcher found exposed units accepting “admin” as the username and the current date as the password, which matches a publicly documented flaw in certain Danfoss controllers that CISA flagged back in May 2025. Updated firmware already fixes it. Many of the affected units were end-of-life models that stopped receiving security updates years ago, and thousands more remain exposed right now.

So how do you keep this from happening to you? Start by accepting that your refrigeration controller, your thermostat, your door access panel and your security cameras are all computers, and every one of them needs the same discipline you give your servers. Nothing operational should be directly reachable from the open internet. Remote vendor access belongs behind a VPN with multi-factor authentication, not a web login anyone in the world can find in thirty seconds. Default credentials have to go. Firmware has to be current, and gear that no longer receives security updates has to be replaced on a schedule instead of running until it fails.

Just as important, your alarms should not depend on the device being attacked. If the controller can be told to stay quiet, you need independent temperature monitoring that reports somewhere else entirely. Along the Gulf Coast we already know what a lost freezer costs after a storm takes the power for three days. The difference here is that no weather event was involved, and no insurance adjuster is going to call this an act of God.

This is exactly the kind of overlooked risk Cyclone 365 helps local businesses find before someone else does. Our team maps every connected device on your network, locks down remote access for your vendors, keeps firmware current, segments operational equipment away from the systems that run your business, and monitors the whole thing around the clock. For restaurants, grocers, seafood processors, clinics and cold storage operators across the Southeast United States, that protection costs a fraction of one ruined freezer.

The groups behind these attacks still have not been identified, and no one has demanded a ransom. Experts lean toward sabotage, though one noted it could just as easily be someone bored and curious, given how little skill it took. Either answer should worry you. Give Cyclone 365 a call and let us make sure your equipment is not the next easy target. Call or Email us today!

Personal Devices at Work Need Clear Rules

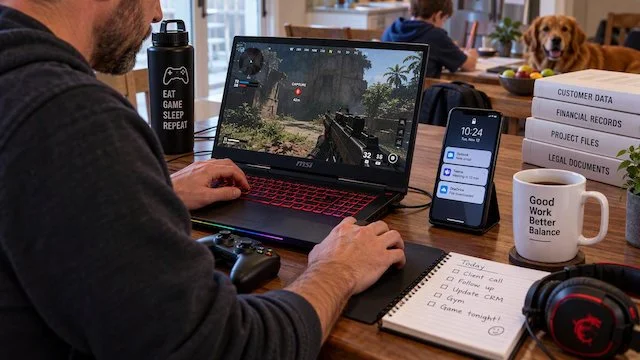
Most businesses never actually decide to allow personal devices. It just happens. Someone adds work email to a phone, saves a customer file to a home laptop, or signs into a company app from a computer the whole family uses. By the time anyone notices, company data is sitting on devices the business does not control.

That is the real issue with bring your own device, usually shortened to BYOD. Once business information lands on a personal phone or computer, you lose visibility into updates, installed apps, backups, and who else uses that device. You also lose an easy way to remove your data when the device is lost or the employee moves on.

What Counts as BYOD

BYOD covers far more than email on a phone. It includes signing into Microsoft 365 or Google Workspace, joining meetings, opening customer files, using a business messaging app, and reaching accounting, CRM, or project management systems from a personal computer. Depending on the application, your information may stay in the cloud or quietly download to the device as attachments, cached data, and saved files.

What You Cannot Control

On a company-owned device, your IT team sets the rules. On a personal device, the employee decides which apps get installed, when the operating system updates, and who else logs in.

Shared household computers are a common blind spot. The UK National Cyber Security Centre advises against allowing BYOD access when an employee cannot keep work separate from other family users. Missing updates are another, since a device may be running an unsupported version of its operating system without anyone knowing.

Downloaded files create a longer tail of risk. A document saved from work email can sit in a Downloads folder, get swept into a personal cloud backup, or be opened in an unmanaged app that makes yet another copy. Personal apps chosen by the employee may also have permission to read files, contacts, or clipboard contents. And when a personal phone goes to a repair shop, saved sessions and business email can go with it.

Decide What Work Is Allowed

The smarter approach is to set access based on the work being performed. You might allow reading email through an approved mobile app while requiring a company computer for anything involving customer data exports, financial records, health information, or legal documents.

Administrative work belongs on a managed device, full stop. Anyone responsible for user accounts, security settings, backups, or core business systems should not be doing that from an unmanaged personal computer. Contractors should follow the same rules, with access limited to exactly what their work requires.

Set Minimum Security Requirements

Before a personal device touches company information, it should meet a baseline. That means a supported operating system still receiving updates, automatic installation of those updates, a screen lock with automatic timeout, and full device encryption. The Australian Cyber Security Centre recommends full-device encryption whenever personal devices may store business information.

Multifactor authentication should be required for email, cloud storage, and any important system. Rooted or jailbroken devices should be blocked entirely. Employees need to know which applications are approved for work, and shared computers need a separate user account for the employee that nobody else can access.

Use Managed Apps and Work Profiles

Device and application management services help keep work information separate from personal information. Mobile device management applies settings to an enrolled device and reports whether it meets your requirements. Mobile application management controls supported work apps and their data, often restricting copying, blocking saves to personal storage, and removing company information on demand.

Microsoft Intune, for example, can pull company data from protected applications when a device is lost or an employee leaves, while personal photos and messages stay untouched. The limitation is important: selective removal only reaches data the service actually manages. A file already copied into a personal backup is gone from your reach.

Put It in Writing

A workable BYOD policy answers the obvious questions before they become urgent ones. Who may use personal devices, which devices qualify, what work is permitted, which apps are required, whether files can be downloaded, what the business can see and remove, what happens when a device is lost or an employee leaves, and who pays for data and repairs.

Have it reviewed for each location where you employ people, and have employees accept it before access is granted.

Gulf Coast businesses deal with enough unpredictability already, between storm season and staff working from wherever they happen to be that week. Your device policy should not be one more thing left to chance. Cyclone 365 helps businesses figure out what their employees can already reach, close the gaps, and put proper management in place so personal devices stay useful without becoming a liability.

If your team is already using personal devices for work, it is worth finding out exactly what that means. Reach out to Cyclone 365 and we will help you sort it out. Call or Email us today!
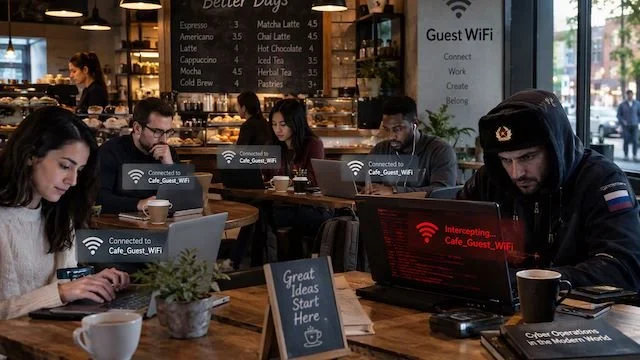
Guest Wi-Fi Should Never Touch Your Business Network

Offering Wi-Fi to customers, contractors, and visitors is just good hospitality. But the phones and laptops those people carry should never share a network with your business computers, printers, security cameras, servers, and file storage.

Even when you trust the person, you do not control their device. You have no idea whether it has current security updates, whether it is carrying malware, or who else has been using it.

A properly configured guest network gives visitors internet access while blocking their devices from reaching anything on your internal network. That includes business computers and servers, network printers, file storage and backup devices, security cameras, building access systems, and your router’s management pages. Both networks can share the same internet connection. The separation happens inside your router, firewall, switches, and wireless access points.

A different Wi-Fi name does not mean the networks are separated. Those names are called SSIDs, and a second SSID proves nothing on its own. The settings behind it have to place guest devices on their own network and block them from reaching private addresses. Business equipment typically handles this with a separate virtual network, known as a VLAN, paired with firewall rules. Some small-business routers do it automatically when guest mode is turned on, and some do not. Look for settings labeled guest network, network isolation, deny local network access, client isolation, VLAN, or guest firewall rules.

Guest devices should also be blocked from talking to each other. This is called client isolation, and it is a separate control from business-network separation. One keeps visitors away from each other. The other keeps visitors away from you. A business guest network should use both.

Personal phones and laptops that only need internet access belong on the guest network. If employees use personal devices to reach company files or applications, you need a clear bring-your-own-device policy covering security software, device management, encryption, and access rules. Smart TVs, speakers, thermostats, and digital displays usually belong on a restricted network too, since they need the internet but have no business reaching your computers.

Here is what to verify. Confirm that managed equipment is on the business network and everything else is on the guest network. Confirm that guest devices cannot reach printers, storage, cameras, servers, or management pages. Enable client isolation if your equipment supports it. Use WPA3 where available, or WPA2 when it is not, with a guest password that is different from your business password. Keep firmware current, replace default administrator credentials, and retire equipment that no longer receives security updates.

Most small businesses along the Gulf Coast do not need a second internet connection for visitors. A capable business router or firewall can keep both networks separate on a single line, and you can cap guest bandwidth so visitor traffic does not slow down your team. Older consumer routers are the common exception, since many offer a guest option with very little control over what guests can actually reach.

Finally, keep the guest password separate and change it when too many people know it, after a large event, or when a contractor no longer needs access. The password controls who connects. It does not replace network separation.

If you are not certain your guest Wi-Fi is truly isolated, Cyclone 365 can test the configuration and tell you exactly what visitor devices can reach. Call or Email us today!

Big Projects Make Big Targets

Most people picture a breach as something loud. Locked screens, a ransom note, systems down. That version still happens, but it is no longer where most of the money goes.

The FBI’s 2025 Internet Crime Report logged $20.9 billion in reported losses across more than one million complaints, a 26 percent increase in a single year. Business email compromise accounted for roughly $3 billion of that from just 24,768 complaints. That is 2.5 percent of all complaints filed, producing about 15 percent of all reported losses, with an average loss of $123,005 per incident.

Put plainly, business email compromise is the largest single source of reported losses among attacks aimed at organizations. And 86 percent of that money moved by wire transfer or ACH, meaning these attacks are not landing in spam folders. They are landing inside real financial workflows and clearing.

Everyone is on the same playing field

This is the part that catches people off guard. A city government, a mid-sized manufacturer, a six-person contracting firm, and a startup still working out of a shared office all face the exact same attack. The email looks the same. The method is identical. The only thing that changes is the dollar amount on the wire.

Attackers are not sorting targets by size. They are sorting by opportunity. A large organization has bigger payments, but a small one often has fewer approval steps, no monitoring, and nobody positioned to question an invoice at 4:45 on a Friday. Being small is not cover. In many cases it is the advantage the attacker is counting on.

How it actually works

The simplest version starts with credentials. An attacker gets a valid username and password through a convincing phishing page, then logs in and changes nothing. They sit in the mailbox, read months of correspondence, learn your vendors, your tone, your approval chain, and your payment cycles. When a routine invoice is due, one arrives with updated banking details at exactly the right moment.

Multifactor authentication helps, but it is not the wall people assume it is. Session cookie theft has become one of the most effective ways around it. Once you sign in, your browser holds a token proving you already authenticated. Modern phishing kits sit between you and the real login page and capture that token as it is issued. Infostealer malware pulls the same tokens straight off an infected machine. The attacker then walks into your account as a fully authenticated session, no password prompt and no MFA challenge, because as far as the system is concerned you already passed both.

The quieter version never touches email at the start. An attacker gets a foothold somewhere nobody is watching and waits. A single unpatched workstation in an office nobody uses. A personal phone with company mail on it. A network printer, a security camera, a smart thermostat, a point of sale terminal, a shop floor sensor, or a router a vendor installed years ago and never updated. These devices rarely support endpoint protection, rarely get patched, and almost never get reviewed. They are permanent, quiet, and connected to everything.

From that foothold, patience does the work. The attacker maps the network, learns which machines matter, harvests credentials and session tokens as people sign in, and moves sideways until they reach an account with signing authority. Mandiant’s latest incident response data puts the median time an intrusion sits undetected at 14 days, and that is the midpoint, not the ceiling. Nothing technically breaks, so nothing alerts. By the time a fraudulent payment request goes out, it comes from inside a real account, references a real project, and lands in the middle of a real conversation.

AI has sharpened all of it. Spoofed domains, cloned writing styles, and voice impersonation now put a fraudulent request within a hair of the genuine article. Victims reported more than $30 million in email fraud losses involving AI in 2025, and since that figure depends on victims recognizing AI was used, treat it as a floor rather than a measurement.

Why the old model fails

Most organizations that get hit are not careless. They have antivirus. They have a firewall. They have someone reliable who keeps the network running. What they usually do not have is anyone whose actual job is to assume an attack is already underway.

The break/fix model made sense when threats arrived on disks and the worst outcome was a dead hard drive. One capable generalist could cover it. That person is still valuable, but asking them to simultaneously run identity governance, email authentication, device inventory, around the clock monitoring, payment controls, and incident response is asking one person to be an entire security department. Reactive support cannot catch an attack that never triggers a support ticket.

What actually stops it

Verification that happens outside of email. Any change to banking details, and any transfer above a set threshold, gets confirmed by phone to a number you already had on file, never a number supplied in the request. It costs nothing to implement at any size, and it is the control that breaks the attack at the exact moment it pays off.

Behind it sits the rest of the stack. Phishing-resistant multifactor authentication that cannot be relayed, along with conditional access and short session lifetimes so a stolen token stops working quickly. Email authentication configured properly so your domain cannot be convincingly spoofed. A real inventory of every device on the network, with the unmanaged ones segmented away from anything that matters. Continuous monitoring that flags unusual mailbox rules, impossible sign-in locations, and new devices appearing where they should not. A written response plan that gets executed in minutes, not days. The FBI’s recovery team froze $679 million for victims in 2025 with a 58 percent success rate, and that outcome depends almost entirely on how fast the fraud is caught. Wire recalls work inside a short window and then stop working at all.

The local picture

Gulf Coast organizations are not too small or too far off the map to be worth targeting. Attackers are opportunistic and they follow money that moves on a schedule. Construction and contracting, port and logistics operations, healthcare practices, real estate closings, and professional services all generate the kind of routine payments that make this work.

Cyclone 365 helps Gulf Coast organizations of every size close those gaps, from Microsoft 365 hardening and identity protection to device and network visibility, continuous monitoring, phishing defense, payment verification policy, and response plans built to move in minutes. The goal is not to replace the person keeping your systems running. It is to put real security infrastructure behind them so one convincing email cannot undo years of work. Need help? Call or Email us today!

We provide IT support and services in and around these areas:

Mobile, AL Pensacola, FL Pascagoula, MS
Daphne, AL Fort Walton Beach, FL Gautier, MS
Fairhope, AL Destin, FL Ocean Springs, MS
Foley, AL Panama City, FL Biloxi, MS
Gulf Shores, AL Tallahassee, FL Gulfport, MS
Orange Beach, AL Lake City, FL Pass Christian, MS

★ Copyright © MMXXI. All rights reserved. ★