
When Your Website Turns Against Your Customers
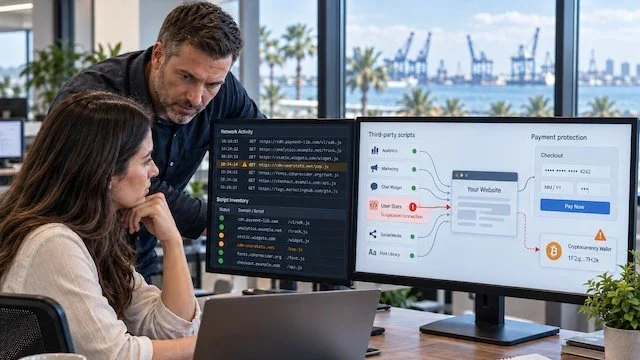
Last Monday, visitors to CNN, the BBC, Zoom, IKEA, HSBC and roughly 175 other well known websites loaded malicious code without a single one of those sites being hacked directly. The code arrived through Optimizely Web Experimentation, a legitimate service these companies use to test changes on their pages. An attacker found a flaw in the platform and quietly added a loader to the custom JavaScript field inside customer projects, leaving the rest of each script untouched. The script still came from the vendor’s own servers with the vendor’s own certificate, so every browser that loaded it trusted it completely.
What that code did is the part worth paying attention to. It swapped cryptocurrency wallet addresses in page text, forms, links and even the clipboard, replacing them with the attacker’s addresses whenever they appeared near words like deposit or send. It also captured card numbers, expiration dates and CVV codes submitted through site forms and shipped them off to the attacker. On iPhones and iPads, it loaded a second stage identified as an iOS exploit kit. Researchers tracked roughly $7,000 in crypto reaching the attacker’s wallets in about nine hours. Optimizely has since patched the flaw and removed the code.
The lesson here is not that Optimizely is uniquely risky. The lesson is that every third-party script on your website is a door into your visitors’ browsers, and you did not install the lock. Analytics tags, chat widgets, ad pixels, A/B testing tools and marketing scripts all run with the same permissions as your own code. When one of those vendors is compromised, your site becomes the delivery mechanism, and your customers are the ones holding the bag.
For businesses here along the Gulf Coast, that risk is not theoretical. A regional contractor, clinic or retailer running a handful of marketing scripts faces the same exposure as a global news network, just without a security team on standby. A few practical moves make a real difference. Audit which third-party scripts your site actually loads and remove the ones nobody uses anymore. Keep marketing and analytics tags off checkout pages entirely, and take payment details through your processor’s own hosted fields in a cross-origin iframe, which this attack could not read. Deploy a Content Security Policy with strict script and connection rules. Rotate API tokens and review who has write access to your marketing platforms. If you accept card payments directly on your site, know what you would tell customers if a day like Monday happened to you.
Cyclone 365 handles exactly this kind of work for businesses across the Gulf Coast, from website and infrastructure hardening to endpoint protection, monitoring and incident response. Supply chain attacks succeed because they exploit trust that was reasonable to extend. The fix is not paranoia. It is visibility into what your systems are actually running and a plan for the day something goes wrong. If you are not sure what is loading on your site right now, that is a good place for us to start. Call or Email us today!