
Personal Devices at Work Need Clear Rules
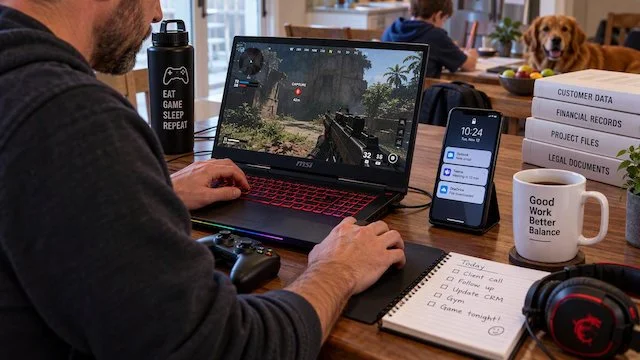
Most businesses never actually decide to allow personal devices. It just happens. Someone adds work email to a phone, saves a customer file to a home laptop, or signs into a company app from a computer the whole family uses. By the time anyone notices, company data is sitting on devices the business does not control.
That is the real issue with bring your own device, usually shortened to BYOD. Once business information lands on a personal phone or computer, you lose visibility into updates, installed apps, backups, and who else uses that device. You also lose an easy way to remove your data when the device is lost or the employee moves on.
What Counts as BYOD
BYOD covers far more than email on a phone. It includes signing into Microsoft 365 or Google Workspace, joining meetings, opening customer files, using a business messaging app, and reaching accounting, CRM, or project management systems from a personal computer. Depending on the application, your information may stay in the cloud or quietly download to the device as attachments, cached data, and saved files.
What You Cannot Control
On a company-owned device, your IT team sets the rules. On a personal device, the employee decides which apps get installed, when the operating system updates, and who else logs in.
Shared household computers are a common blind spot. The UK National Cyber Security Centre advises against allowing BYOD access when an employee cannot keep work separate from other family users. Missing updates are another, since a device may be running an unsupported version of its operating system without anyone knowing.
Downloaded files create a longer tail of risk. A document saved from work email can sit in a Downloads folder, get swept into a personal cloud backup, or be opened in an unmanaged app that makes yet another copy. Personal apps chosen by the employee may also have permission to read files, contacts, or clipboard contents. And when a personal phone goes to a repair shop, saved sessions and business email can go with it.
Decide What Work Is Allowed
The smarter approach is to set access based on the work being performed. You might allow reading email through an approved mobile app while requiring a company computer for anything involving customer data exports, financial records, health information, or legal documents.
Administrative work belongs on a managed device, full stop. Anyone responsible for user accounts, security settings, backups, or core business systems should not be doing that from an unmanaged personal computer. Contractors should follow the same rules, with access limited to exactly what their work requires.
Set Minimum Security Requirements
Before a personal device touches company information, it should meet a baseline. That means a supported operating system still receiving updates, automatic installation of those updates, a screen lock with automatic timeout, and full device encryption. The Australian Cyber Security Centre recommends full-device encryption whenever personal devices may store business information.
Multifactor authentication should be required for email, cloud storage, and any important system. Rooted or jailbroken devices should be blocked entirely. Employees need to know which applications are approved for work, and shared computers need a separate user account for the employee that nobody else can access.
Use Managed Apps and Work Profiles
Device and application management services help keep work information separate from personal information. Mobile device management applies settings to an enrolled device and reports whether it meets your requirements. Mobile application management controls supported work apps and their data, often restricting copying, blocking saves to personal storage, and removing company information on demand.
Microsoft Intune, for example, can pull company data from protected applications when a device is lost or an employee leaves, while personal photos and messages stay untouched. The limitation is important: selective removal only reaches data the service actually manages. A file already copied into a personal backup is gone from your reach.
Put It in Writing
A workable BYOD policy answers the obvious questions before they become urgent ones. Who may use personal devices, which devices qualify, what work is permitted, which apps are required, whether files can be downloaded, what the business can see and remove, what happens when a device is lost or an employee leaves, and who pays for data and repairs.
Have it reviewed for each location where you employ people, and have employees accept it before access is granted.
Gulf Coast businesses deal with enough unpredictability already, between storm season and staff working from wherever they happen to be that week. Your device policy should not be one more thing left to chance. Cyclone 365 helps businesses figure out what their employees can already reach, close the gaps, and put proper management in place so personal devices stay useful without becoming a liability.
If your team is already using personal devices for work, it is worth finding out exactly what that means. Reach out to Cyclone 365 and we will help you sort it out. Call or Email us today!